By Massive IT · March 1, 2026
Download Case Study PDF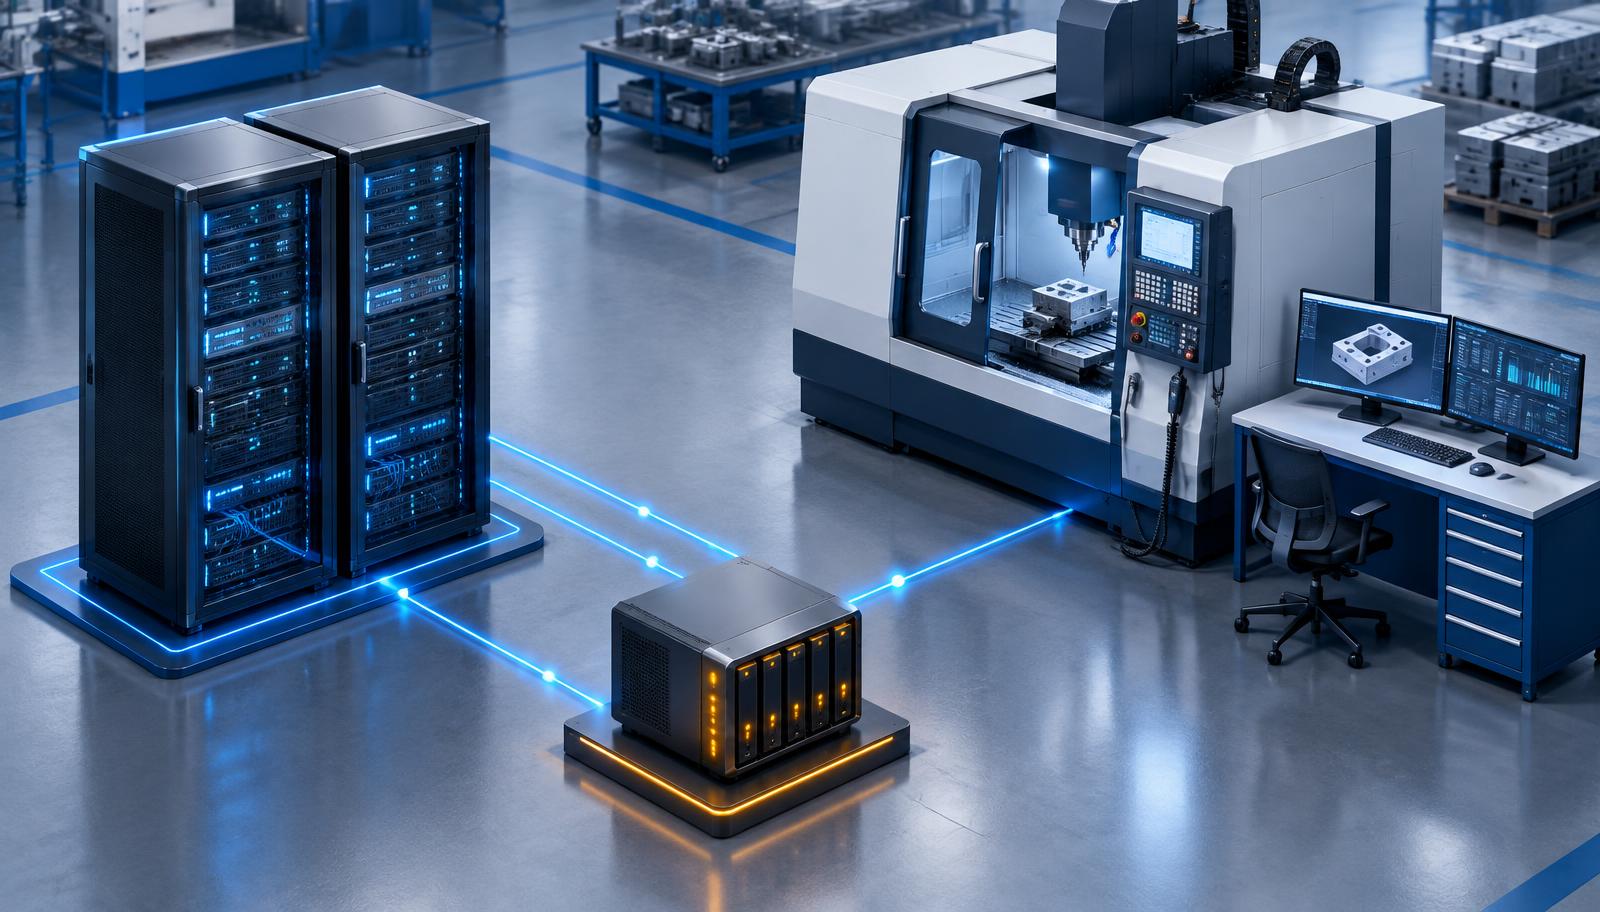
Project snapshot
| Detail | Summary |
|---|---|
| Customer | A precision manufacturing company (customer anonymized) |
| Production dependency | CNC milling machines paired with workstations running specialized control applications |
| Identity environment | Legacy on-premises Microsoft Active Directory |
| Incident | Domain authentication failure disrupted production access |
| Recovery approach | Restore a viable system state backup, reconstruct the domain, and establish healthy domain controllers |
| Case study date | March 2026 |
The challenge: an identity failure became a production outage
A precision manufacturer’s CNC equipment depended on dedicated workstations and specialized milling control applications. When those workstations rebooted and could no longer authenticate against the domain controllers, operators lost access to the applications required to run production.
The supplied project account describes a legacy Active Directory environment degraded by deferred maintenance. The resulting authentication failure had an immediate operational impact: an infrastructure problem prevented the production floor from functioning normally.
Customer revenue, workforce statistics, and other identifying business details have been omitted. This case study reflects the supplied project account, not a universal recovery guarantee.
Evaluating the rebuild recommendation
According to the supplied case study, Microsoft Premier Support initially recommended rebuilding the domain. That route would have required substantial workstation and application reconfiguration. The customer engaged Massive IT for a second assessment of whether a viable recovery path remained.
Massive IT worked with the support team to understand the failure, then evaluated the domain topology, replication health, and available backup state. The objective was to restore authentication and production access while avoiding a wholesale rebuild where a safe recovery was feasible.
The recovery strategy
1. Assess domain health and stop propagation
Engineers audited domain controller topology and replication to identify the failure conditions. The account describes a coordinated shutdown of affected domain controllers to prevent continued replication of the damaged directory state.
2. Restore a viable system state backup
Massive IT identified a usable system state backup from approximately three months earlier and restored a single domain controller to a known-good configuration. The backup’s age was a material recovery consideration; the supplied account does not establish that all directory changes made after that backup were preserved.
3. Reconstitute and validate the domain
The team reconstructed the Active Directory environment from the restored controller, validating directory integrity through the recovery process. New healthy domain controllers were then built and promoted to restore redundancy.
4. Test the production dependencies
Workstation re-authentication testing checked that users could sign in and launch their applications. CNC control workstations were included because successful directory recovery alone would not demonstrate that the production floor was operational.
5. Confirm the operational handoff
The supplied case study reports that production access was verified before the environment was returned to the customer. This connected the technical recovery to the business function affected by the incident.
Project outcomes
| Area | Reported result |
|---|---|
| Active Directory | Directory environment recovered and healthy domain controllers established |
| Workstation access | Authentication and control-application access restored |
| Production | CNC production operations restored |
| Rebuild scope | No workstation rebuilds reported in the supplied case study |
The central outcome was a recovered identity environment that allowed the manufacturing operation to resume, without the workstation rebuild path initially contemplated. The source does not provide a measured recovery duration, independently verified financial savings, or a complete data-loss assessment, so none is claimed here.
Results depend on the specific failure, backup integrity, directory state, application dependencies, and recovery scope. A successful recovery in this engagement does not establish that recovery is preferable to rebuilding in every incident.
Documented engineering, not a generic runbook
The supplied account reports that Microsoft Premier Support requested the recovery procedures following case closure. It does not independently establish their adoption into Microsoft training, labs, or official guidance. This case study therefore makes no Microsoft endorsement or training-adoption claim.
The recovery sequence is summarized to explain the engagement, not to instruct readers to shut down or restore their own domain controllers. Active Directory recovery requires environment-specific planning, supported procedures, and qualified engineering review.
Why this project matters
Industrial systems often rely on ordinary identity services in ways that are not obvious until authentication fails. This project illustrates the importance of understanding application dependencies, evaluating available recovery evidence, and validating the production workflow rather than stopping at server health checks.
Massive IT combined directory engineering, backup evaluation, coordinated recovery, and production-focused validation to address the customer’s operational problem.
Assess your recovery readiness
Massive IT helps organizations assess identity infrastructure, backup readiness, and critical application dependencies. Schedule a consultation or call (813) 518-5454.